
Your Everyday Work Account Has Too Much Power
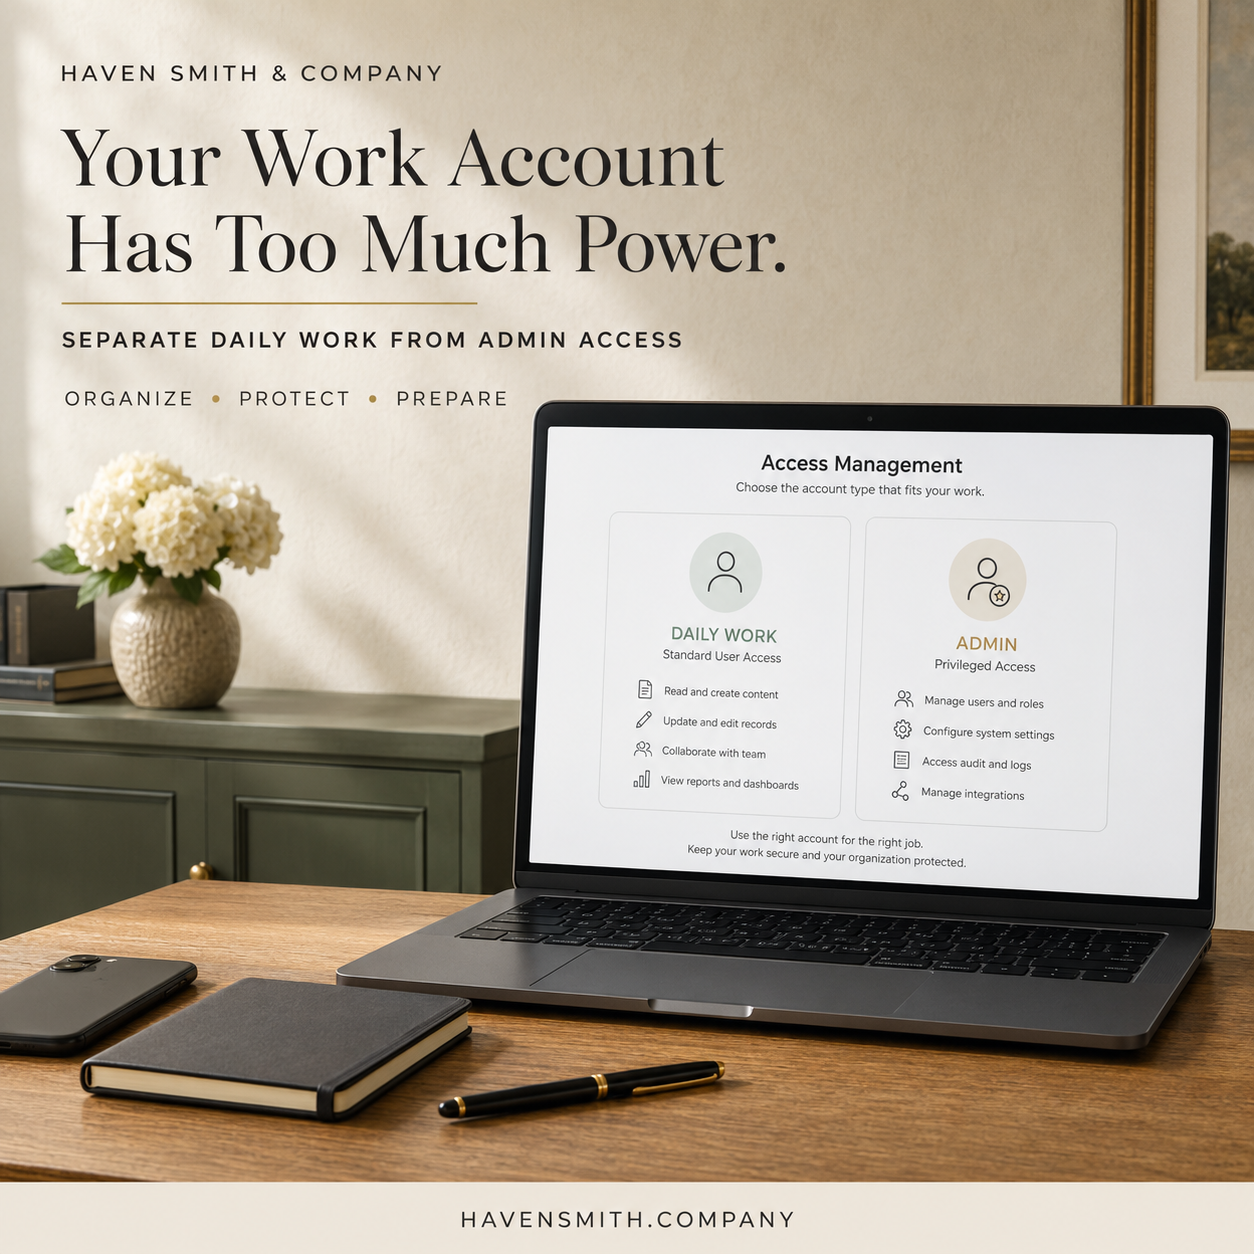
Separate routine work from administrator access before one mistake or compromised account affects the entire organization.
The account you use to read email, open attachments and browse the internet may also have permission to change billing, add users, remove security controls and control your organization’s most important systems.
That arrangement feels convenient—until the account is compromised.
An ordinary phishing message, malicious attachment or reused password becomes significantly more dangerous when the affected account has administrative privileges.
The solution is not to eliminate administrator access. It is to reserve that power for the limited tasks that genuinely require it.
If You Read Only One Thing
Use a standard account for everyday work and a separate, strongly protected administrator account for installations, permissions, billing and system changes.
Your Action Steps
Choose one important business platform.
Identify everyone who currently has administrator or owner access.
Determine whether each person still needs that level of authority.
Create or use standard accounts for routine work.
Reserve administrator access for specific administrative tasks.
Protect privileged accounts with strong multifactor authentication and current recovery information.
Document who owns the platform and how continuity will be maintained.
What Administrator Access Actually Means
Administrator, owner and super-administrator roles may allow a person to:
Add or remove users
Change permissions
Reset passwords
Access organizational data
Install software
Change security settings
Connect third-party applications
Modify billing
Transfer or delete assets
Remove other administrators
The exact permissions vary by platform, but the principle remains the same: the account can make changes affecting other people and the organization itself.
That power should not be treated as an ordinary convenience.
Apply Least Privilege in Plain Language
The principle of least privilege means giving a person only the access needed to complete assigned work.
It does not mean distrusting employees or making every task difficult. It means matching authority to responsibility.
A person who publishes social posts may not need control over account ownership and billing. A contractor who updates a website may not need permanent access after the engagement ends. A bookkeeper may need financial information without needing to control the organization’s email system.
Access should be:
Appropriate to the task
Assigned to a named person
Limited in duration when possible
Reviewed regularly
Removed when no longer needed
Separate the Person From the Role
A named employee and an administrative role are not the same thing.
Instead of allowing a single everyday account to carry permanent administrative power, maintain:
A standard named account for daily work
A separate administrator account for privileged tasks
The administrator account should not be used for ordinary email, casual browsing or routine document work.
This separation reduces exposure. If the daily account is compromised, the attacker may not automatically gain the authority to control the entire platform.
Protect Administrator Accounts More Carefully
Administrator accounts deserve stronger safeguards because the consequences of compromise are greater.
Use:
A unique, strong password
Strong multifactor authentication
Current recovery information
Limited trusted devices
Security alerts
Documented ownership
A reviewed continuity plan
Do not share one administrator username and password among several people. Shared credentials make it difficult to determine who changed what, remove one person’s access or respond effectively to a security incident.
Audit More Than Your Email Platform
Administrator privileges may exist across your entire organization.
Review:
Email and productivity systems
Website and domain accounts
Bookkeeping and payment platforms
Cloud storage
Social media
Scheduling tools
Customer-management systems
Online stores
Advertising accounts
Security and backup services
Pay particular attention to former employees, former contractors, duplicate accounts and people who received elevated access for a short-term task.
Do Not Create a Single Point of Failure
Restricting access does not mean allowing only one person to understand an essential system.
Your organization needs a documented continuity plan identifying:
The platform owner
The current administrators
The recovery process
The billing owner
The location of relevant agreements
What happens if the primary administrator is unavailable
The goal is controlled access with continuity—not uncontrolled access or dependence on one person.
Outside Resources
Haven Smith & Company Resources
Build practical organizational safeguards with the Digital Safety course.
Bring digital life management education to your team through a Haven Smith & Company workshop.
Use a Digital Life Strategy Session to review one platform, ownership question or continuity concern.
Not sure where to begin? Take the free two-minute quiz and get the one thing to do next.
Choose one platform today. Identify every administrator, remove unnecessary privileges and make sure ordinary work is being completed through ordinary accounts.
Free · Two minutes
Where does your digital life stand?
Nine questions on organizing, protecting and preparing. You get your level and the one thing worth sorting out first.
Take the free quizFree · Nine questions · No account needed